


SOP, ISO & DOCUMENTATION / WORKFLOW 38
AI Internal Audit & Evidence Management
Make audit evidence easier to organise. Keep every conclusion with an accountable reviewer.
AIGreen Plus can scope an assistant for Malaysian manufacturers that turns approved audit criteria into draft checklists, groups supplied evidence and keeps corrective-action follow-up visible. It supports reviewers; it does not certify conformity, replace auditors or decide findings.
Human review retainedIntegration subject to discoveryFictional dashboard concept
See the dashboard concept ↓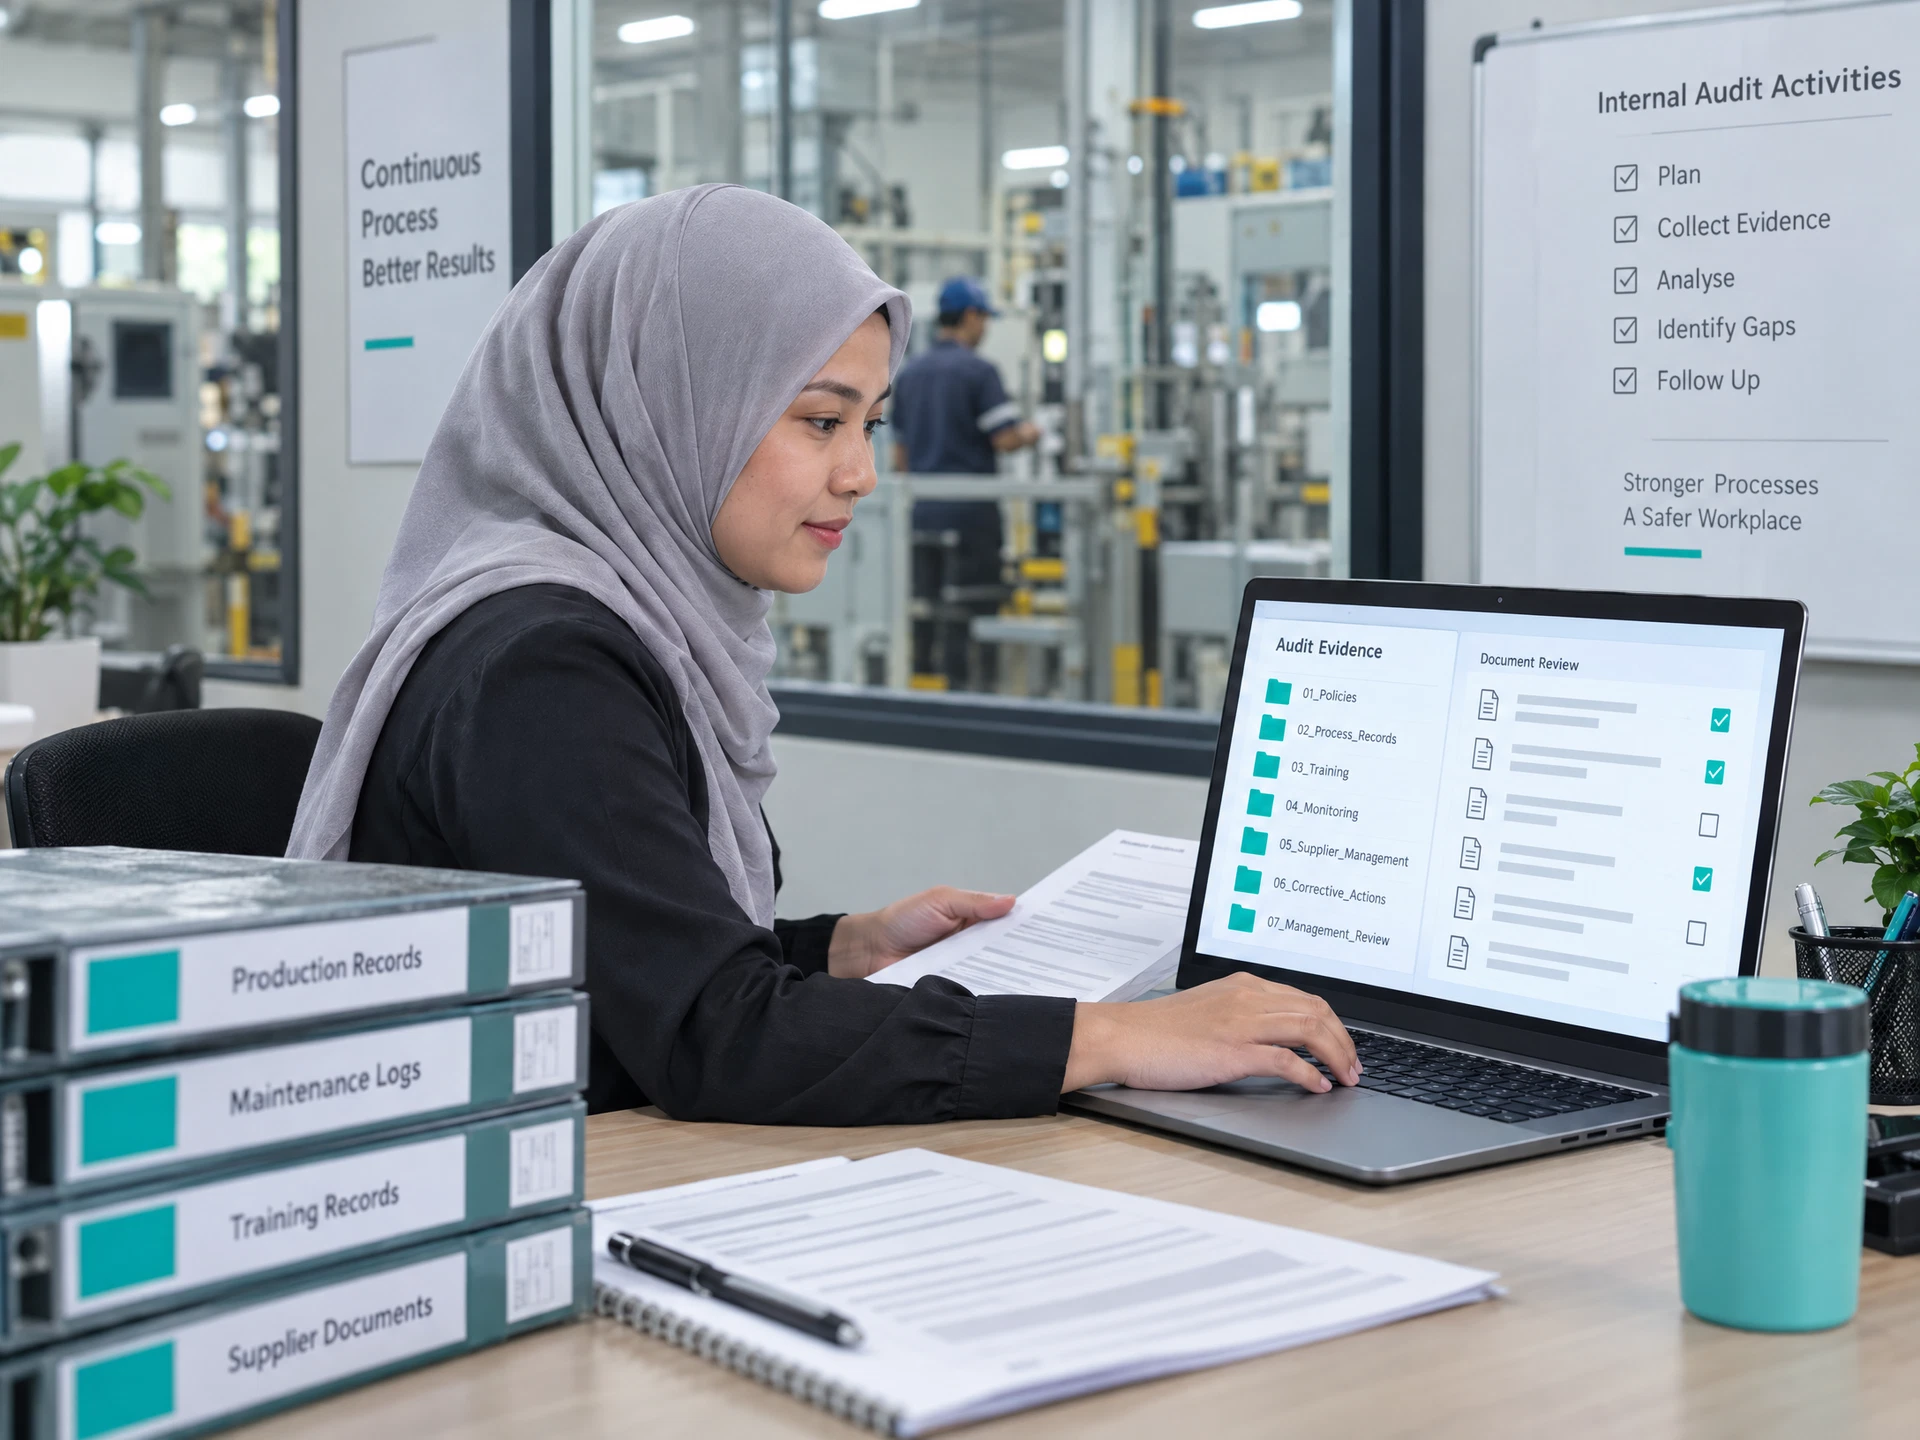
Image status: generating — final scene not yet confirmed.
This workflow helps internal-audit teams turn approved requirements into a draft checklist, connect anonymised records or document references to each requirement, highlight missing or unclear evidence, and maintain corrective-action status. It suits quality, document-control and department owners in a Malaysian manufacturing setting. A qualified auditor or authorised process owner reviews sources carefully, confirms findings, approves wording and decides any action before the record is used.
01 / SEE THE OUTPUT
Internal Audit Evidence Review Board
FICTIONAL SAMPLE / four requirement areas in a draft quarterly audit queue. A clear view of the records, calculations and exceptions your team may need to review.
PROPOSED DASHBOARD CONCEPT
FICTIONAL SAMPLE / four requirement areas in a draft quarterly audit queueInternal Audit Evidence Review Board
Evidence references by requirement area
Fictional sample values · Bars compare fictional evidence-reference counts for three displayed requirement areas; they are not audit performance, certification or customer results.
Unit: evidence items
| Requirement area | Evidence items (count) | Review status | Action owner | Review date |
|---|---|---|---|---|
| Document control | 6 | Ready | Document controller | 2026-03-04 |
| Competence records | 5 | Ready | Training coordinator | 2026-03-05 |
| Internal findings | 4 | Needs review | Quality manager | 2026-03-06 |
| Corrective actions | 3 | Ready | Process owner | 2026-03-07 |
AI-assisted draft / requires verification
In this fictional queue, three requirement areas are marked Ready and one needs reviewer action. The draft points to evidence-reference counts only; it does not infer a root cause, conformity status or final audit decision.
02 / THE WORKFLOW
Five steps, with an accountable owner.
The example separates deterministic checks from AI-assisted drafts, exceptions and decisions.
- 01↓
Define audit scope
Confirm sites, processes and criteriaAgree the audit boundary, period, approved criteria and named reviewers before drafting.
OWNER / CONTROLAudit programme owner / scope approval - 02✓
Map requirements
Build a traceable draft checklistTurn the supplied requirement list into checklist items with evidence expectations and status fields.
OWNER / CONTROLInternal auditor / criteria control - 03≡
Gather evidence
Link approved records by requirementOrganise authorised document references, records and interview notes while retaining source context.
OWNER / CONTROLProcess owner / evidence submission - 04◎
Review exceptions
Separate gaps from unclear sourcesSurface missing, duplicate, outdated or ambiguous references for qualified human verification.
OWNER / CONTROLQualified auditor / finding review - 05↗
Approve and track actions
Close the loop with accountable ownersRoute draft findings and corrective actions for approval, due dates, updates and closure evidence.
OWNER / CONTROLAuthorised manager / action approval
If a check fails: Hold the record for its owner, correct the source and preserve the approved manual fallback.
03 / RESPONSIBILITIES
Automate the repetition. Keep the judgment.
| Task | Manual today | Proposed assistance | Human review / owner |
|---|---|---|---|
| Create a checklist from approved audit criteria | Copy requirements into a spreadsheet and add evidence prompts by hand. | Prepare a structured draft checklist with requirement IDs, evidence fields and review status. | An authorised auditor confirms interpretation, scope and final checklist wording. |
| Assemble evidence for each requirement | Search folders, email and shared drives, then record references in separate notes. | Group supplied references by requirement and flag unlinked, duplicate or incomplete entries. | Process owners verify authenticity, currency, relevance and permitted use of each source. |
| Prepare an exception and finding register | Compare evidence manually and rewrite observations into a tracking log. | Draft neutral review prompts and keep observation, evidence and status fields together. | The qualified auditor investigates, classifies and approves any finding; no finding is automatic. |
| Monitor corrective-action follow-up | Send reminders and update action rows across meetings or spreadsheets. | Maintain proposed owners, due dates, status and closure-evidence prompts for review. | An authorised owner accepts the action, verifies effectiveness and approves closure. |
Create one traceable evidence view
Propose a requirement-to-reference structure using only approved sources and access rules agreed during discovery.
Start audits from a consistent draft
Generate a reviewable checklist template from the selected criteria, with version and scope fields retained.
Make reviewer attention visible
Separate missing, outdated and ambiguous evidence prompts so the auditor can decide what requires investigation.
Keep corrective actions accountable
Offer a shared status view for proposed owners, due dates and closure evidence without approving actions automatically.
04 / TRANSPARENT FIGURES
Show the working behind the claim.
These numbers show one hypothetical calculation method. They are not customer evidence.
HYPOTHETICAL WORKED EXAMPLE / NOT CUSTOMER RESULTS
45 → 25 combined labour minutes for the same task.
12 one internal-audit requirement pack reviewed for completeness units per month × 20 minutes less per unit.
8 → 3 per 100 checked error-affected administrative entries, not incidents/accidents/disease/product defect outcomes (5.0 percentage points).
See assumptions and calculations
| Measure | Illustrative calculation | Meaning and limit |
|---|---|---|
| Labour effort | (45 − 25) ÷ 45 × 100 = 44.4% | Same workload and expected review quality; includes ongoing exception checks as scoped. |
| Time capacity | (45 − 25) × 12 ÷ 60 = 4.0 hours | Released time is not payroll savings or guaranteed job reduction. |
| Admin checks | (8 − 3) ÷ 100 = 5.0 percentage points; 62.5% relative | Separate hypothetical like-for-like administrative check of checklist and evidence-register entries, not a safety, certification, product-quality or audit-outcome guarantee. Actual measures require an agreed baseline, sampling method and authorised review. |
Hypothetical same-workload comparison: a reviewer spends 45 minutes manually assembling and checking one requirement pack, versus 25 minutes reviewing a proposed structured draft, including human review and exception effort. It assumes 12 comparable packs per month, unchanged evidence quality and no payroll or headcount conclusion.
Scenario figures are illustrative arithmetic, not benchmarks, forecasts, actual customer results or guarantees. Measure a like-for-like pilot with the same definitions before making a claim.
05 / PROPOSED DELIVERY
Scope one process, then measure it.
Scope and data workshop
Confirm audit criteria, evidence types, reviewer roles, privacy needs, source locations and the manual fallback before any draft is configured.
What you receiveSigned-off scope note, field list and sample-data planEvidence taxonomy and checklist design
Design requirement, source-reference, status, observation, action and approval fields around the selected internal-audit process.
What you receiveTraceability map and reviewable checklist prototypeControlled sample review
Run anonymised or approved sample records through the proposed flow and test missing-source, duplicate, outdated-version and access cases.
What you receiveTest log, exception register and reviewer feedbackHandover and operating agreement
Document approval gates, ownership, retention, support boundaries, change control and how corrective-action closure will be evidenced.
What you receivePilot-readiness pack and written operating decision06 / BEFORE YOU INVEST
Inputs, boundaries and ownership should be clear.
What to prepare
- Approved audit criteria, requirement register and scope supplied by the internal-audit or quality manager
- Anonymised document references, revision dates and evidence metadata supplied by document control
- Authorised process records, training or inspection evidence selected by each process owner
- Existing finding and corrective-action register with owners, dates and statuses, sanitised where needed
- Reviewer roles, approval rules, access list and retention requirements confirmed by the Malaysian site owner
What to agree in writing
- The workflow prepares drafts and prompts only; a qualified auditor or authorised process owner decides evidence sufficiency, findings, conformity and closure.
- Only the least necessary approved or anonymised records should be used; access, retention, hosting and Malaysian privacy review require written agreement.
- No automatic certification, regulatory conformity statement, product release, safety decision or corrective-action approval is produced.
- Interfaces with document stores, spreadsheets or existing systems, plus licences, testing, training and manual fallback, are scoped and agreed separately.
- Any recurring support, change control, audit-period coverage and response expectations are commercial and operational terms to be documented, not assumed.
Confidence comes from traceable evidence.
Define the baseline and acceptance criteria before a pilot, trace outputs to approved sources, record review and exception effort, and make a scale/revise/stop decision with the process owner.
07 / CLEAR ANSWERS
10 questions. Practical answers.
Clear answers
Frequently asked questions.
Ten workflow-specific questions on scope, integration feasibility, controls, costs and measurement.
What does AI Internal Audit & Evidence Management actually prepare?
It can prepare a draft checklist from approved criteria, organise authorised evidence references by requirement, flag incomplete or unclear source links, and maintain a corrective-action view. The output is a review aid, not an audit opinion. A qualified auditor confirms observations, findings, wording and closure decisions.
What information should a Malaysian manufacturer provide first?
Start with the audit scope, approved requirement list, evidence categories, sample document metadata, current finding or action fields, reviewer roles and access rules. Anonymised references or synthetic samples can be used for design. Do not provide personal or confidential material until the access and handling approach is agreed.
Can this work with our existing folders, spreadsheets or QMS?
A scoped workflow may use exports, agreed file structures or an approved interface, depending on the system and permissions. AIGreen Plus does not assume a particular integration or claim a ready-made connector. Discovery should confirm formats, identity controls, testing, manual fallback and who maintains the connection.
Who is responsible for approving evidence and audit findings?
Your designated internal auditor, quality manager or other authorised role remains responsible under your governance. The workflow may organise references and draft neutral prompts, but it cannot determine whether evidence is sufficient, classify a nonconformity, approve a corrective action or declare closure.
Do the illustrative labour figures mean we can remove audit staff?
No. The scenario is a hypothetical time comparison for one administrative requirement pack and includes human review. Any released time should be measured against an agreed baseline and may support better preparation or follow-up; it is not a promise of payroll savings, job elimination or reduced professional accountability.
Are the dashboard numbers actual customer audit results?
No. The dashboard is explicitly a fictional sample with non-personal rows created to show how evidence counts and review statuses could be displayed. It is not customer evidence, a benchmark, a certification result or a measured outcome. Your team would define real measures and approve the sampling method.
How are security, access and privacy handled?
The design should use least-necessary data, role-based access, approved retention and anonymisation where practical. A qualified Malaysian review of privacy, confidentiality, hosting and records requirements is needed before live use. Those controls require written scope and testing; this workflow is not a compliance promise.
How soon can we reach a usable milestone?
Timing depends on scope, source quality, reviewer availability, system access and testing needs. A sensible milestone is an agreed scope and checklist prototype, followed by controlled sample review. No duration is promised here; AIGreen Plus can propose dates after discovery and written acceptance criteria.
What affects the quotation or recurring cost?
Drivers may include the number of sites and criteria, source formats, data preparation, integration or export work, access controls, testing, training, change requests and support ownership. There is no fabricated price in this record. A written proposal should separate one-off scoping from any recurring service or licence costs.
Who owns ongoing updates and support after handover?
The operating agreement should name the owner for criteria changes, evidence taxonomy, reviewer access, corrective-action fields, testing and escalation. Support hours, response expectations and update responsibilities are not assumed to be 24x7. Agree them in writing, with a manual process available when the workflow is unavailable.
START WITH ONE REPEATABLE TASK
Discuss the workflow ↗Discuss Internal Audit & Evidence Management for your operation.
Share the process and the type of information involved—not confidential records. We can discuss discovery, access boundaries and an agreed way to measure a scoped pilot.
New AI-created images are fictional scenes; the production-reporting photograph is licensed Pexels stock. None depicts actual AIGreen Plus staff, clients, facilities, workflows or results.
All dashboard values and benefit scenarios are fictional; the screen is not a live integration. Workflows, system access, privacy, responsibilities, licences, costs and support require written scope. No ranking, savings, staffing, safety, quality or compliance outcomes are guaranteed.
